
The founders behind EMP Intake.
We spent years inside the enterprise security industry, running video surveillance, access control, and incident response, and handling evidence directly with investigators, law enforcement, and attorneys.
We watched strong cases fall apart at the evidence / intake layer. EMP Intake is the local-first software we wish we'd had. And we sell it to you direct.
EMP Intake and Document Naming Manager (DNM) are products of Falcrex Systems Inc.
Read how the two products fit together →
Evidence should speak for itself. We build the tools that make sure it can.
EMP Intake exists because the most preventable reason investigations fail has nothing to do with what was captured on camera or logged by an access control system. It has everything to do with what happened to that evidence afterward: files nobody named, handling nobody logged, a package nobody can prove was untouched.
We build evidence intake software for the people who know a solid case and a defensible case are two different things. EMP Intake covers the evidence layer end to end: structured intake, timeline reconstruction, chain-of-custody documentation, and a verifiable export package.
Every file hashed, every audited action attributed, every custody transfer verifiable.
BUILT IN VANCOUVER, BRITISH COLUMBIA · BUILT FOR EVIDENCE-CRITICAL WORK
Two people. You can email either of us.
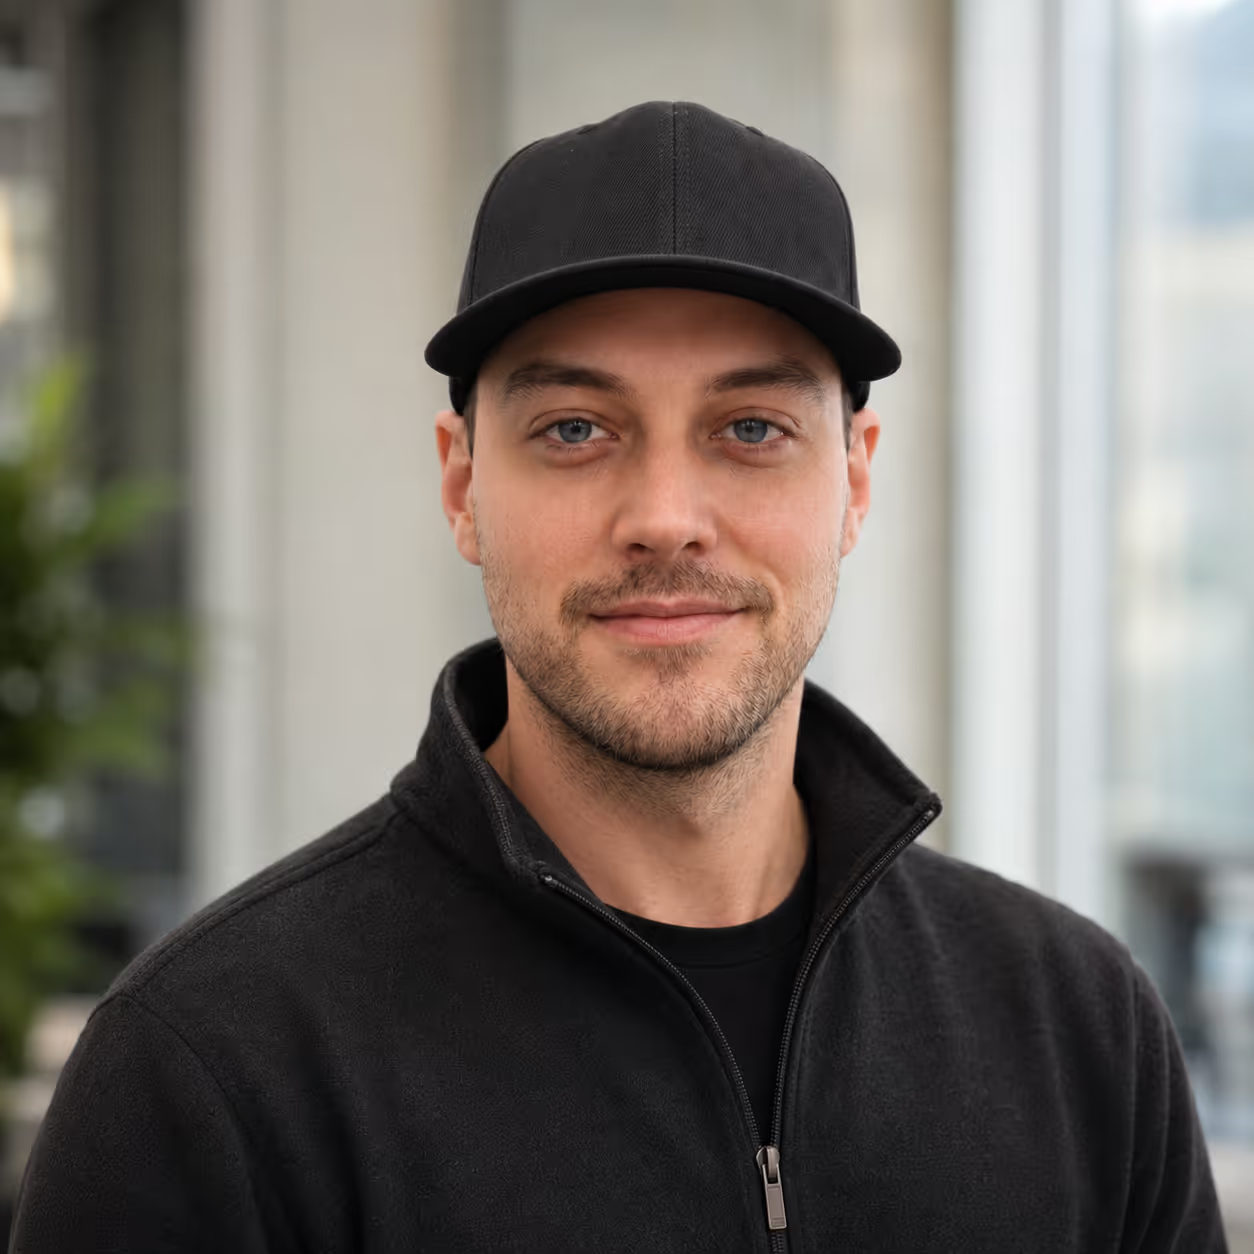
Brendan has spent fifteen years on the front line of physical security from installations to incident response. That’s the work EMP Intake was built for.
He started as a service tech, went on to work for technical support at a Fortune 500 security company and left as a Senior Technical Support Escalation Specialist, owning the hardest cases under strict SLAs. When a video, access-control, or integrated security system broke in the field, it reached his desk.
From there Brendan moved into corporate security and IT leadership in regulated environments: Head of Security, then Director of Security & IT, across Health Canada licensed operations. He investigated internal and external thefts, wrote reports for law enforcement and regulators, and ran incident management systems across multiple sites. He didn’t read about the evidence problem in a whitepaper. He felt exactly where the documentation broke down.
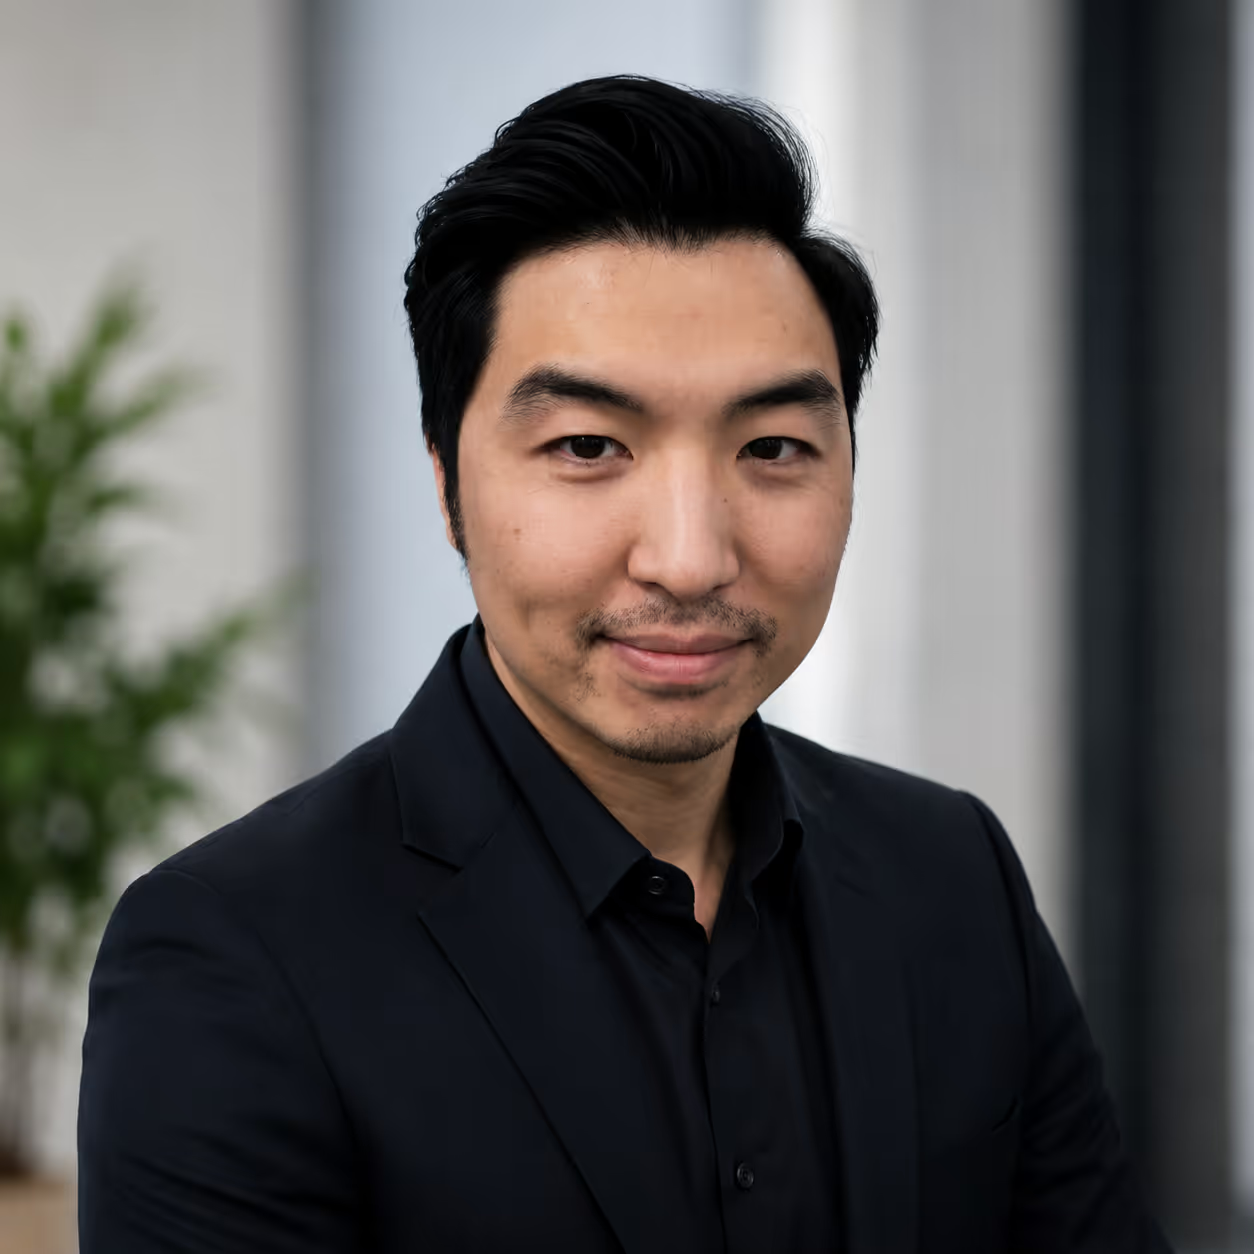
Before co-founding EMP Intake, Jason spent seven years at a Fortune 500 organization in video surveillance and access control. He worked his way up from the support desk to Senior Manager of technical support and product escalation for the Americas, where the toughest escalations landed on his team.
That work put him alongside investigators, law enforcement, attorneys, and prosecutors, compiling evidence for subpoenas and active cases. He lived the problem EMP Intake solves and escalated it himself, and he heard firsthand what success looked like from the people whose careers depended on getting it right.
One thread runs through all of it: knowing where systems break down, where documentation fails, and where the gap between what happened and what can be proven does real damage. EMP Intake is our answer to that gap.
One advisor. Thirty years on the other side of the table.
Theo brings more than 30 years in law enforcement, investigations, corporate security, and risk management to EMP Intake. His career spans federal policing, organized crime, civil forfeiture, intelligence, undercover operations, asset protection, regulatory compliance, and polygraph examination, leading multidisciplinary teams through complex and sensitive matters across government, law enforcement, corporate, and international environments.
Theo was Brendan's boss for four years and has been a steady sounding board since. He knows what an investigation needs from its evidence before it reaches a prosecutor, a regulator, or a courtroom, and he has seen from the other side of the table what happens when the intake layer fails.
As an advisor and trusted consultant, Theo helps us pressure test EMP Intake against how investigators, security teams, and enforcement agencies actually work, and how they evaluate new tooling. Outside his full-time role, he runs Liar Liar Polygraph Services in Abbotsford, British Columbia as a licensed Polygraph expert.
From the front line to evidence intake.
The front line
Both founders came out of the enterprise physical security world. Across different customer bases, they watched the same failure repeat: strong investigative work undermined at the intake layer.
The pattern
Evidence questioned in court because the metadata was wrong. Originals quietly overwritten on a shared drive. No reliable way to prove who touched a file, or when. The work was good; the intake was the problem.
EMP Intake Workstation
They started empintake.com and built the workstation edition first: SHA-256 at intake, originals preserved, a continuous audit log, and an export package counsel can verify without our software installed.
EMP Intake Teams
The same chain-of-custody discipline, multi-user, on PostgreSQL you control. Targeting a small founding cohort of pilot organizations for 2027, onboarded directly by the founders.
The principles we build against.
A file is evidence the moment it exists.
Not when it reaches a courtroom. Not when someone remembers to log it. The moment a file is created, it can matter. Integrity has to start at intake, not at export.
Defensible by design, not by discipline.
Chain of custody shouldn’t depend on a person remembering to do the right thing under pressure. In EMP, hashing, preserved originals, and the audit log are structural. They happen because that’s how the software works.
Sell it ourselves. Ship in public.
No reseller chain, no channel team, no support tier you have to fight through. You email us, a founder reads it. We’d rather earn the trust than buy the distribution.
Your data stays yours.
EMP Intake keeps evidence in your environment. EMP Intake Teams is built to run on infrastructure you control, not ours. And because the export format is open and verifies without EMP, your cases stay yours and provable, whether you subscribe or not.
Common questions
Who builds EMP Intake?
Two co-founders: Brendan Foote (CEO) and Jason Chan (COO). Both came out of enterprise physical security, working evidence cases on the front line with investigators and law enforcement. empintake.com is founder-run and sold direct, with no reseller chain and no outside channel team.
Why focus on evidence intake specifically?
Because intake is where chain of custody quietly dies. We watched solid investigations get picked apart over gaps that started the moment a file landed on a shared drive. EMP is built around fixing that one layer well, rather than being a generic case tool that treats integrity as an afterthought.
Is EMP a certified forensic tool?
EMP’s handling is designed to align with NIST SP 800-86 (forensic techniques in incident response) and NIST SP 800-101 (mobile device forensics). Alignment is a design target that shapes the product; it is not a certification claim. SP 800-101 references concern handling and exporting mobile-device evidence acquired elsewhere, not extraction from a device.
How do I reach a founder?
Email hello@falcrex.com. It goes to Brendan or Jason. No ticket queue, no autoresponder. We aim to reply the same business day on weekdays, though we don’t promise a guaranteed response time.
Talk to the people who built it.
Try EMP Intake Workstation on a real case. 14-day trial, no card, no sales call. Or email a founder directly with whatever’s on your mind.
Don't take our word for it, verify a sample export in your browser →
Follow Falcrex on LinkedIn ↗