
Internal investigations, assembled and ready before anyone asks for the file.
Evidence management for internal theft, fraud, and misconduct cases. Prepare the investigation record before legal, HR, insurance, or law enforcement asks for it: every file, hash, and custody entry in one case object you can assemble fast and hand off clean.
When someone asks for the file
When HR, legal, insurance, or law enforcement asks for the file, it has to already be complete. Build it as you work the case, not something you stitch back together from emails and three Word docs with fighting timestamps the week someone asks.
Evidence management software for corporate security is what stands behind an internal theft, fraud, or misconduct investigation when legal, HR, insurance, or law enforcement asks for the file. An internal investigation rarely falls apart over one missing file. It falls apart because the pieces never lived in the same place: badge logs in one export, a CCTV clip on a thumb drive, witness notes in email, the timeline in someone's head. Six months later legal asks who handled what and when, and nobody can say for sure. EMP keeps each physical security incident file in one auditable case, from intake to the briefing on the executive's desk.
Where EMP fits in the workflow.
Your corporate-security packet might include
- ✓ The complaint or report that opened the case
- ✓ Badge and access logs
- ✓ CCTV clips
- ✓ Witness statements
- ✓ The legal hold notice
- ✓ The export for outside counsel
Internal theft & misconduct investigation
Harassment, hostile work environment, threats, internal theft, and fraud. Witness statements, HR notes, exported CCTV clips, and badge logs land in one physical security incident file, and case actions get logged as you go.
Policy violation
Code of conduct, expense fraud, conflict of interest. Email exports, expense receipts, manager statements, and ethics-hotline transcripts come in hashed at intake, so the record stays intact later.
Asset theft & shrink
Inventory-loss inquiries. Apprehension reports, recovery records, and exported video go into one package the DA or civil-recovery firm can check on their own machine.
Vendor & third-party
Vendor fraud, kickback investigations, supply-chain integrity. Procurement documents and communications come in as case evidence, with a visible record of what changed from the moment they arrive.
Insider risk & departures
Pre-M&A integrity reviews, IP-theft inquiries, post-departure investigations. Handle sensitive matters with the export the next reviewer can verify without EMP installed.
How a corporate-security case moves through EMP
- Open the case and pull the source records. Badge-access CSVs, the CCTV clip off the thumb drive, witness emails, and HR files import into one case. Each file is hashed (SHA-256) the moment it lands, so the original is preserved and a working copy is what you actually touch.
- Build the case around people and entities. Tag the subject employee, the witnesses, and the assets involved, and link each piece of evidence to who it implicates, so the badge swipe, the camera, and the statement all point at the same incident.
- Reconstruct the incident on a timeline. On Professional, align imported access-control logs and video in Timeline Recon and the access events line up against the footage, in sequence, instead of living in two systems.
- Generate the Export Package. Professional also supports report branding. One ZIP with selected originals and reports. Enable Manifest for file checksums and the verifier; Standard and Professional can also include Audit Timeline and supported audit data.
- Hand it to legal and they verify it without trusting EMP. Outside counsel building a wrongful-termination defense recomputes the hashes with sha256sum or the /verify tool. If one byte moved since intake, it shows. No EMP install on their end, and the packet verifies on its own.
Feature availability: Standard adds Chain of Custody, Audit Timeline and Incident Maps. Timeline Recon, Link Analysis and custom report branding require Professional. Core includes case management, file intake and exports.
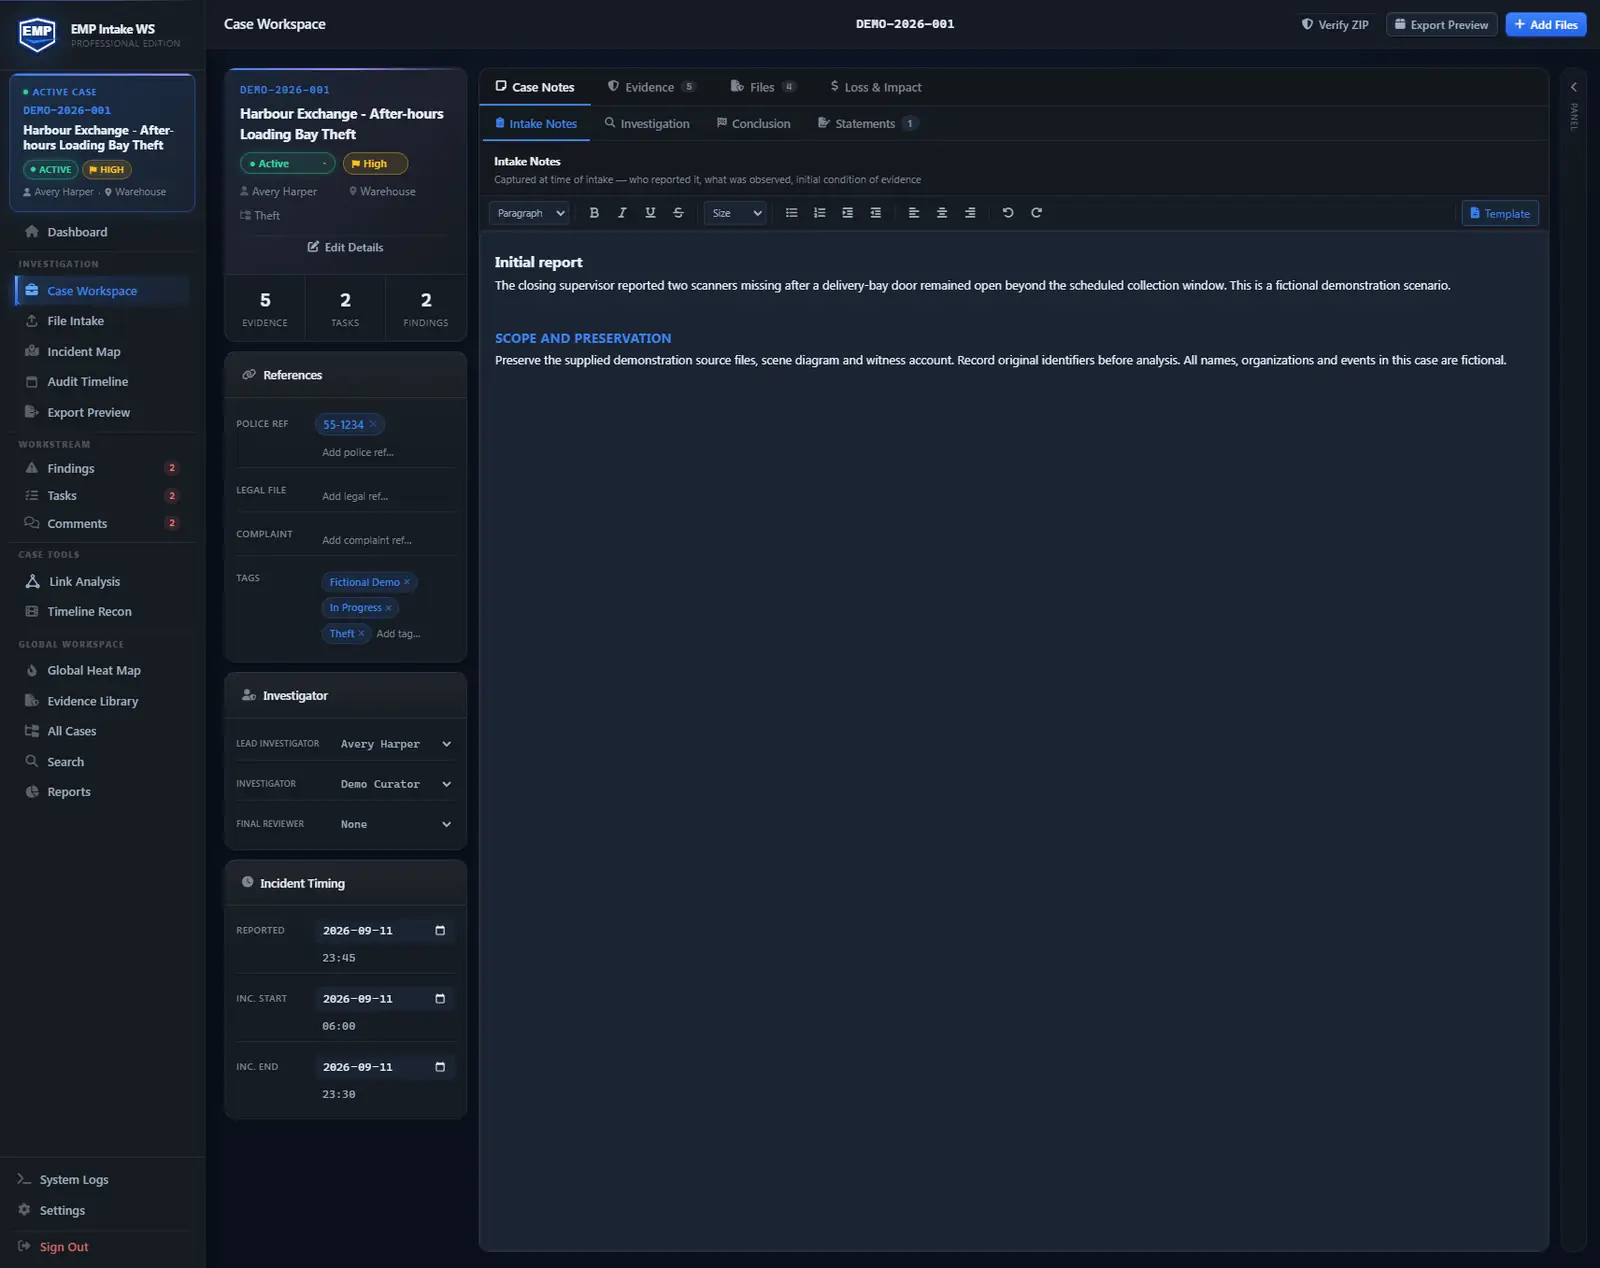
Case workspace example
Workplace theft investigation. Track the employee, the witness, a vehicle, an access card, CCTV clips, badge-reader events, scene locations, and recovered property as case objects. Record loss and impact, link each object to the evidence that supports it, then export a verifiable package for counsel or law enforcement.
Ingests your exports. Doesn't replace your tools.
EMP organizes files exported from access-control, video and HR systems. Import badge logs, CCTV clips, personnel records and witness documents, with preserved originals and recorded handling.
- CSV exports from your access control system, brought in by file import
- Video exported from your CCTV/VMS, imported as case evidence
- CSV or PDF exports from your HRIS, ingested as files
- Email exports (PST, MSG, EML), hashed on the way in
- Export packages outside counsel can open and read on their own machine
Questions these teams ask first.
Is evidence handled this way admissible in court?
No software guarantees admissibility; that call belongs to the court. What EMP gives you is the trail to argue it: hashed originals, an append-only audit log, and a manifest the opposing side can verify on their own.
Can EMP ingest exports from our access-control system?
Export the CSV from your access-control system and bring it in through file import. Each file is hashed (SHA-256) at intake, so it's part of the chain of custody from the moment it enters the case. EMP imports the file. It does not connect to the access-control system directly.
Does my evidence leave my workstation?
No. EMP Intake Workstation runs on a Windows workstation, and the case lives in a SQLite database right there: no cloud upload, no telemetry of file contents. Only three kinds of network call ever leave, and none carry case data: a licensing check on activation and validation, an optional update check, and optional map-resource requests when map views, Timeline Recon playback, or exports use online basemaps. Map requests go through a Falcrex-controlled map delivery service using Cloudflare infrastructure (see the Trust page for details).
How do I hand a case to outside counsel?
Generate a package with selected evidence and reports. Enable Manifest to include file checksums and the standalone verifier. Standard and Professional can include the Audit Timeline PDF and entitled machine-readable audit data. EMP calculates the SHA-256 of the finished ZIP after archive creation and records that value outside the ZIP in the package and export audit records; the exporting party can provide that value when exact-container verification is required. Counsel recomputes the per-file hashes with the packaged verification tool, on the /verify page, or with a standard tool like sha256sum.
How does this compare to Resolver, Case IQ, or NAVEX?
Those are broader SaaS platforms: GRC, workplace-investigation workflow, ethics hotline. EMP Intake WS is narrower and runs on your own workstation, and it focuses on local files, recorded handling and verifiable exports. Compare current capabilities and deployment for your requirements in our EMP and Resolver comparison.
Build the case anyone can verify.
EMP Intake Workstation comes with a 14-day trial, no card and no sales call, so bring a real case and watch it stay defensible.